Every repository. One answer. The depproof hub: self-hosted, cross-repo dependency governance.
The depproof scanner checks one repository. The hub brings every scan together, so the questions that span all of them take one query — on your own infrastructure.
Or write to hello@depproof.com — a real person reads it.
The questions one scan can’t answer
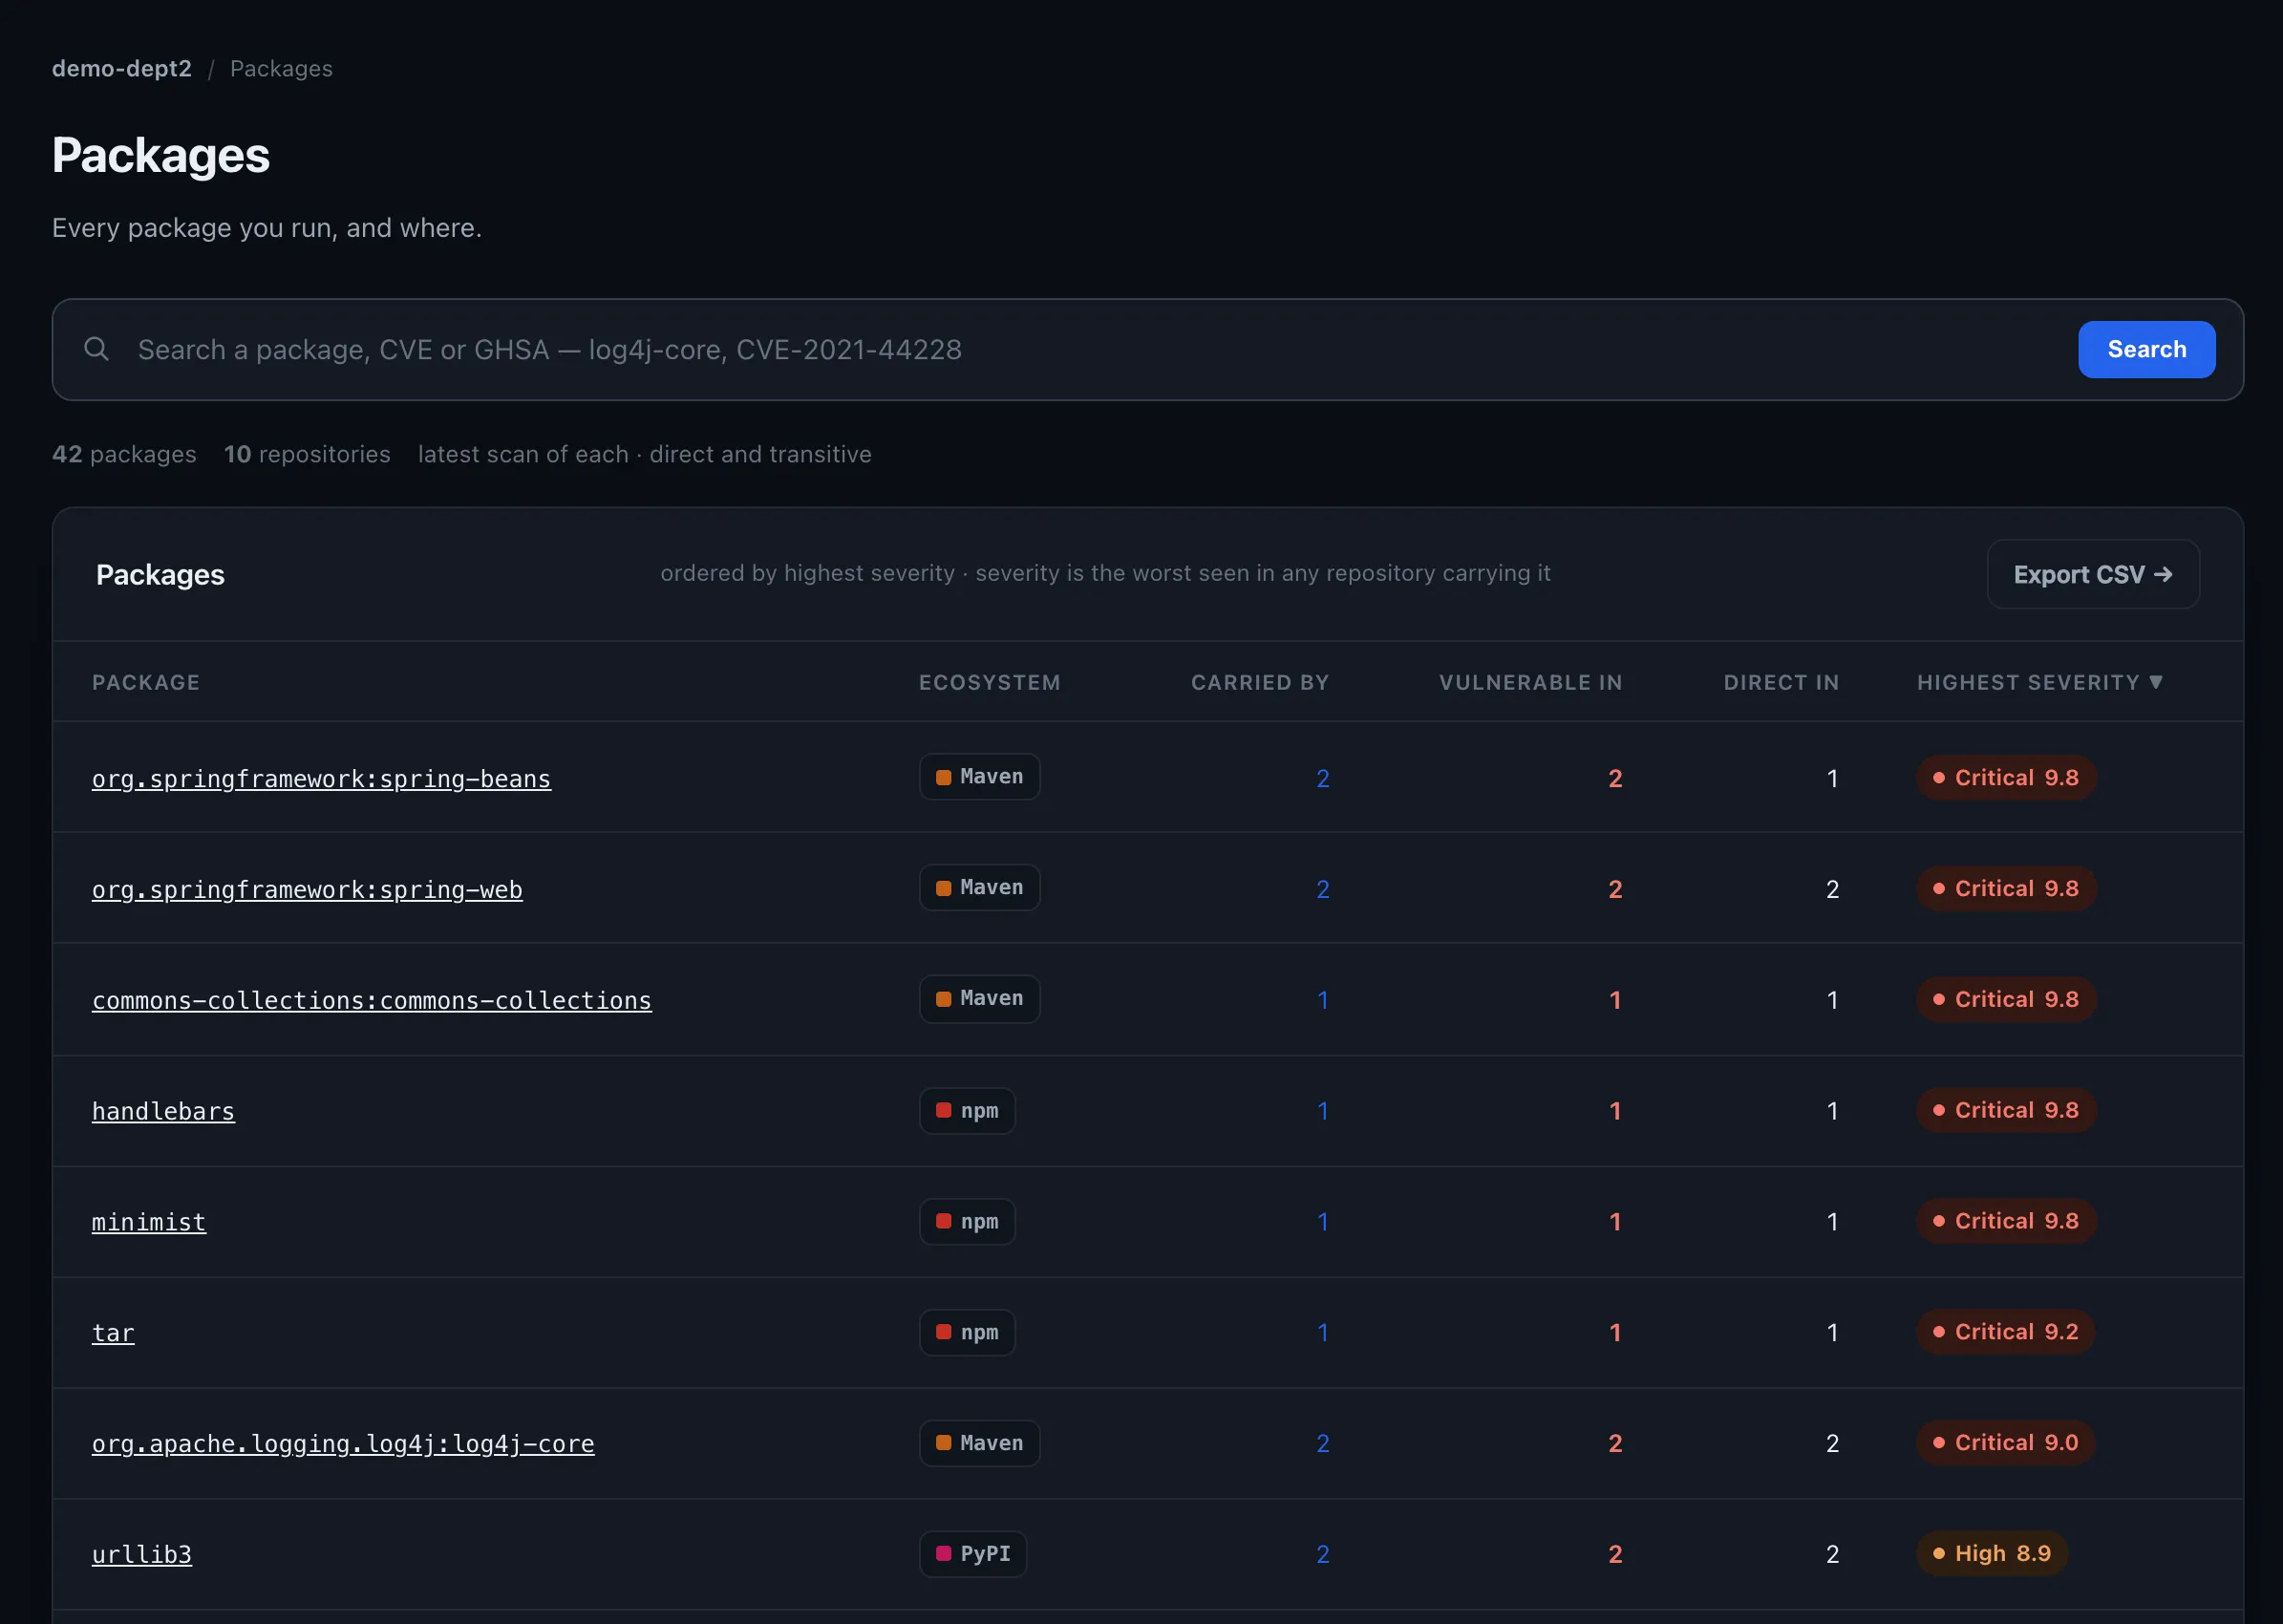
Is this new CVE anywhere?
Blast-radius search across every repository, in one query.
Which products carry a license we prohibit?
Org-wide license posture, copyleft and source-available included.
What’s the current SBOM?
A CycloneDX bill of materials for any product, on request.
Is it still clean?
Every inventory is re-checked against new advisories over time.
Who accepted this risk, and until when?
Waivers with an owner, an expiry and an append-only audit trail.
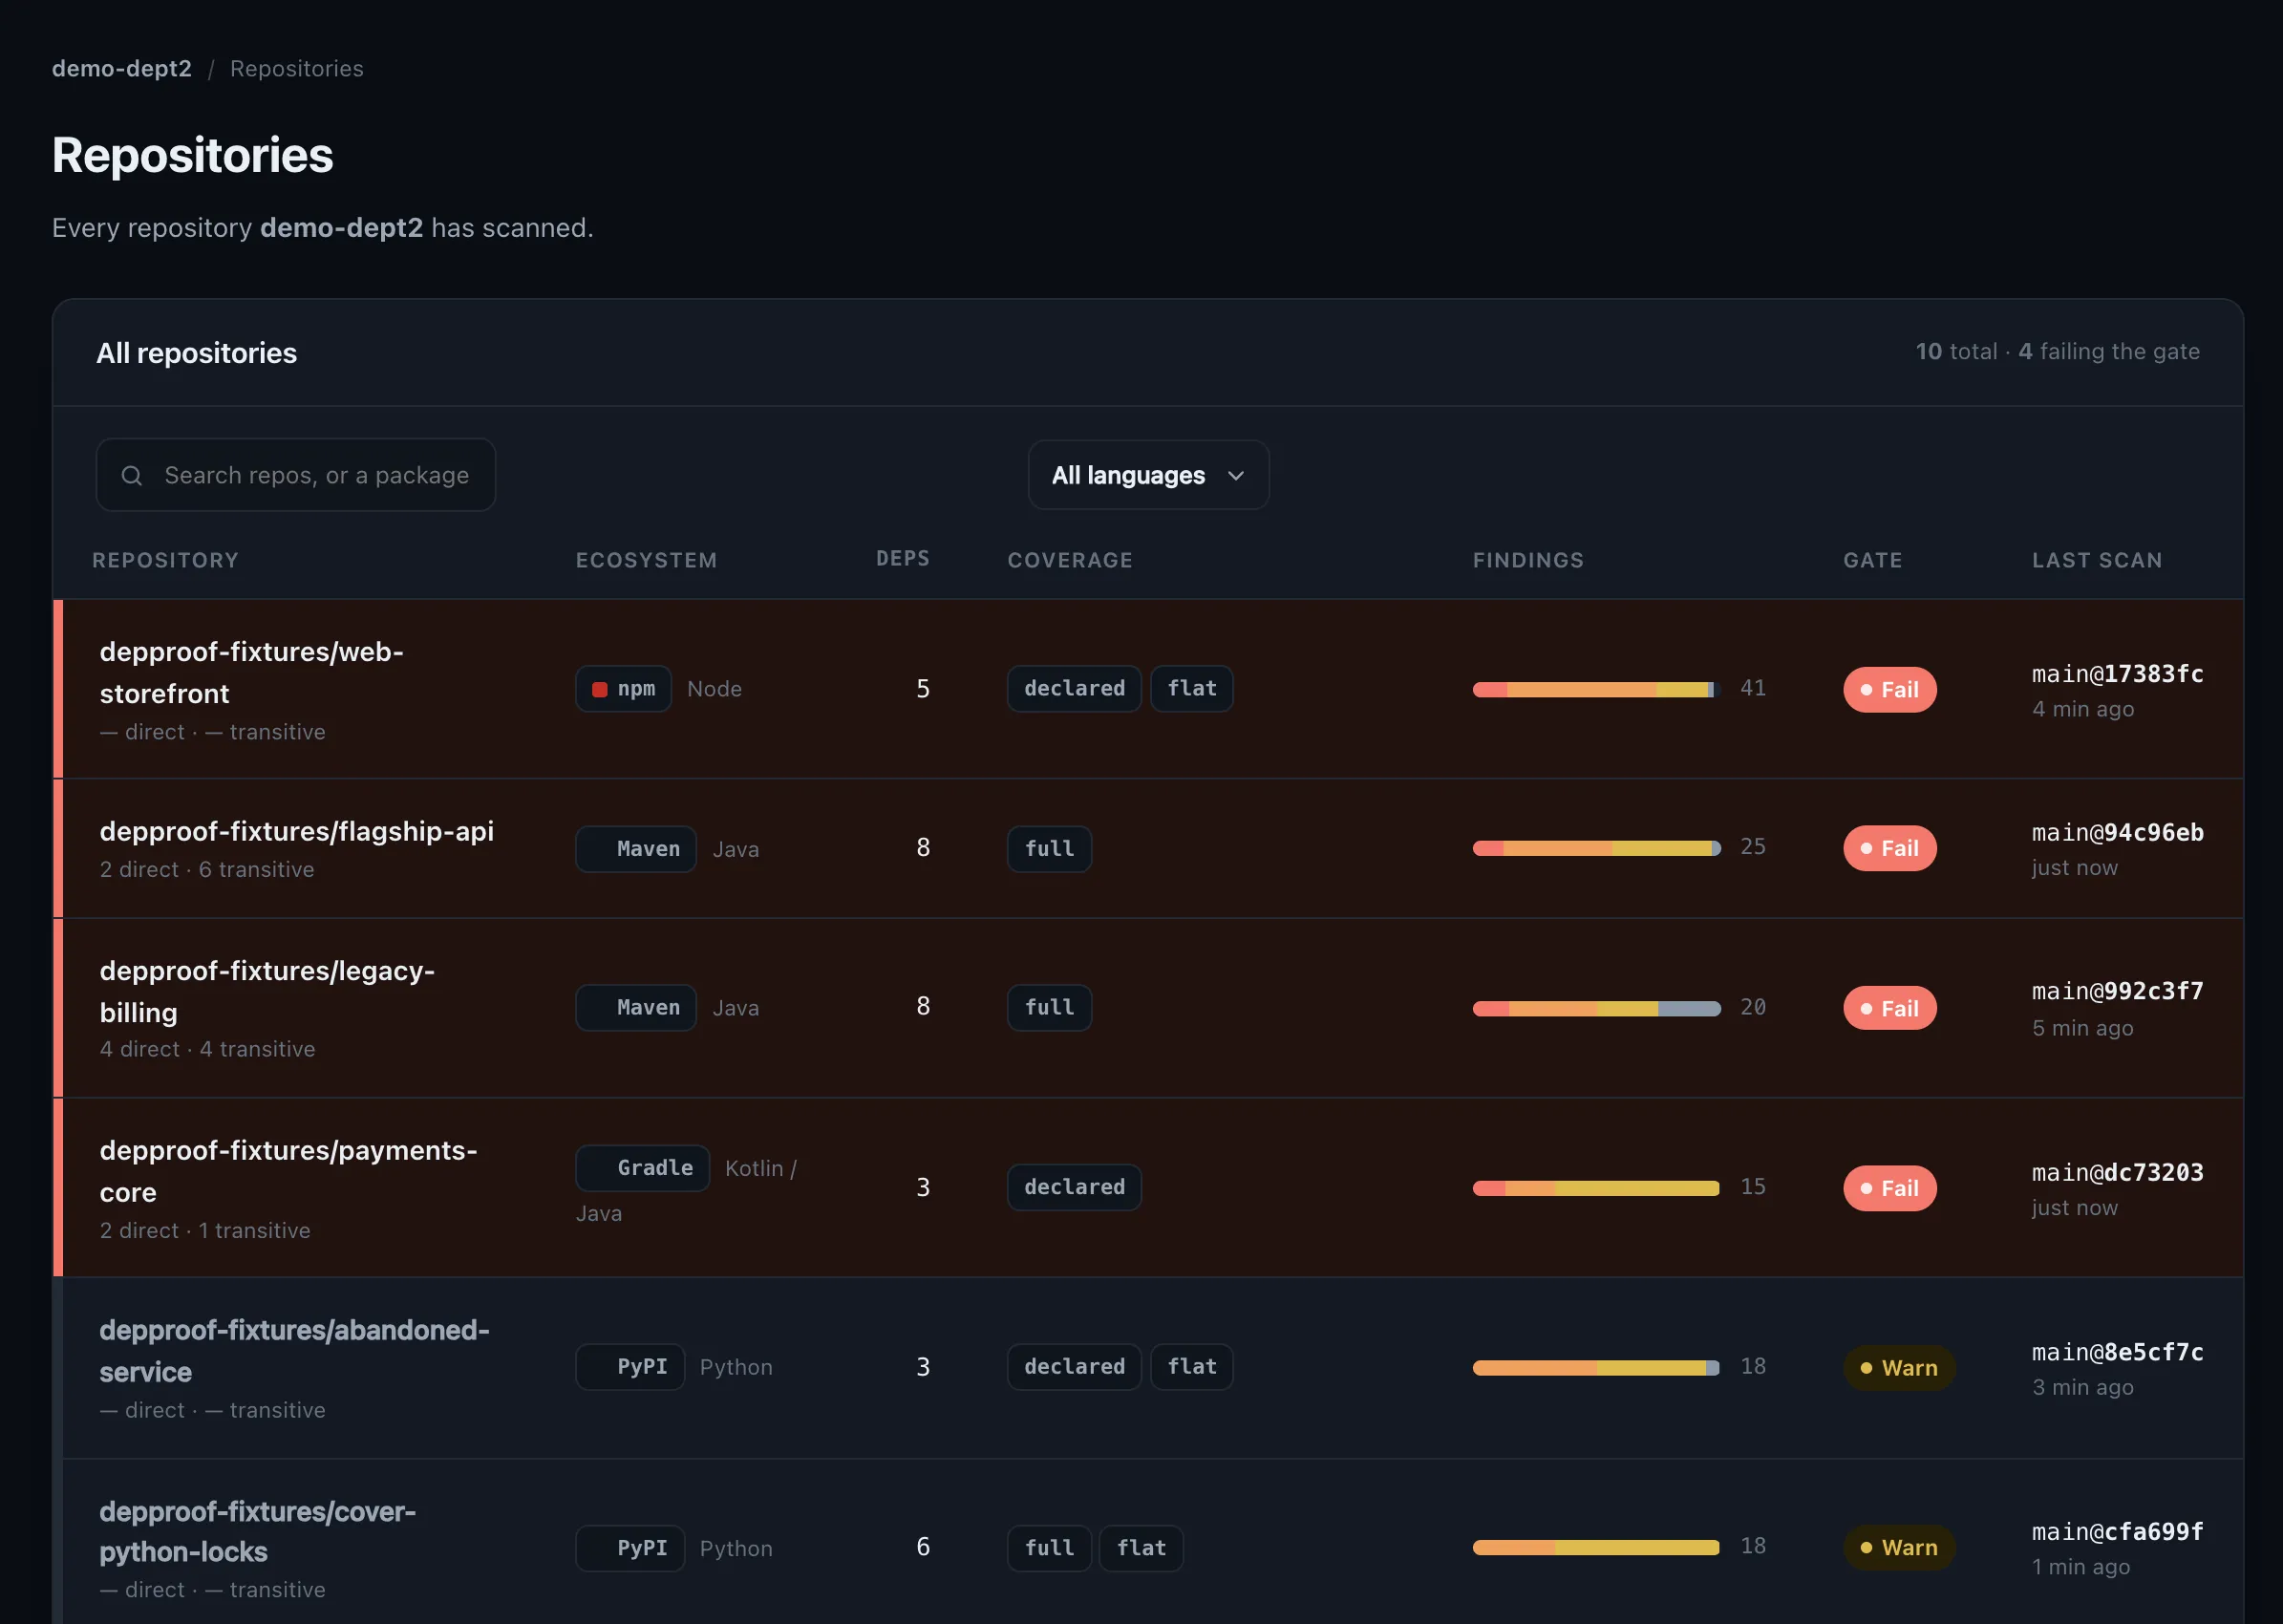
Which repositories did we cover?
Coverage for every repository, shown rather than assumed.
A look inside
Who it’s for
Regulated teams
SOC 2, the CRA and customer questionnaires that ask for an SBOM and proof of monitoring.
Growing estates
More repositories than anyone can keep in their head, and one answer expected across all of them.
Data that stays home
Deployed in your own network, owned by you, with SSO/OIDC. No vendor cloud, no new subprocessor.
Every hub report starts as a software composition analysis scan — a GitHub Action or one container. Start with the Maven SBOM guide, the npm license check or self-hosted SBOMs.
Tell us about your estate
The Hub is a depproof product you add to the Scanner. We’ll be straight with you about fit.
Or write to hello@depproof.com. More answers in the FAQ.